KORV

korv.ai

See the finding. Open the fix. Stop the merge.

KORV is one place for a personal project or a company. It reads the pull request, lists the repositories it scanned, and opens a fix on that repository. A critical finding fails the check named gate.

  1. A bot resizes the database. cursor[bot] changes the payments database from db.t4g.micro to db.m6g.large and raises copies from 2 to 8. KORV says do not merge, and shows the rule that blocks that agent next time.
  2. A token and an old package. The pull request adds a GitHub token and lodash 4.17.20. KORV names the file and says upgrade to 4.17.21. The token value is not copied into the comment.
  3. The same findings, across repositories. Open the portfolio, pick MediaWikiCloudInfra, and use Open fix pull request. That button opens the repository. You still merge it.
In this check What you see
Secrets The file and the kind of secret. The value is not copied into the comment.
Packages A known advisory for a dependency version, with the version to upgrade to.
Dangerous code A shell turned on, code run from text, TLS checks turned off, or a database query built by joining input into the SQL.
Infrastructure and containers An open network rule, public storage, a privileged container, or an image tagged latest.
Tests Application code changed and the diff has no test file. This is not a coverage percentage.
Not in this check A running application, and a cloud account. Those are a later phase. KORV reads repository files today. Dependabot still opens its own pull requests.

A critical finding fails the GitHub job. The merge stops only after branch protection requires that check. Open the portfolio for this GitHub account.

This is a real pull request

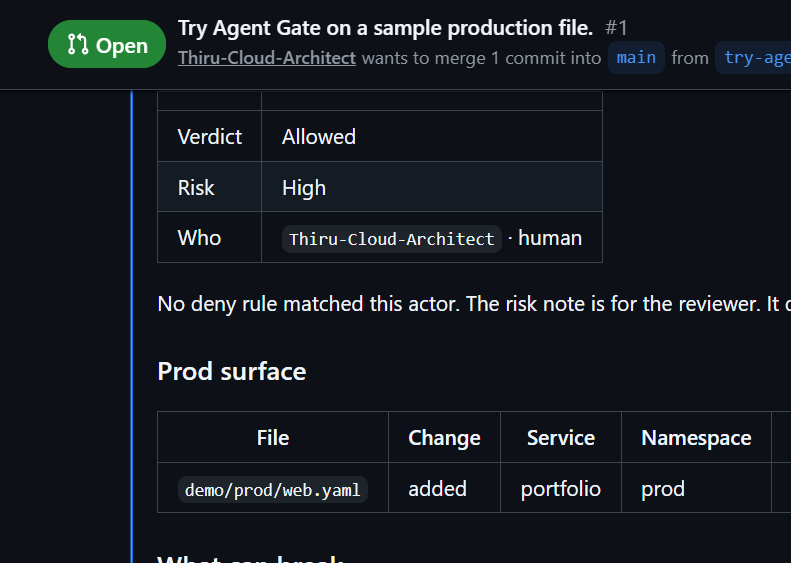
Pull request 1 on online-portfolio-project-samples. A person added demo/prod/web.yaml.

GitHub comment. Verdict Allowed, risk High, opened by Thiru-Cloud-Architect, a person. The production file is demo/prod/web.yaml.
The comment. Allowed means a person opened it, not a blocked bot. High means the new file is production. This picture is from an earlier run, so the heading still says Agent Gate. New comments say KORV.
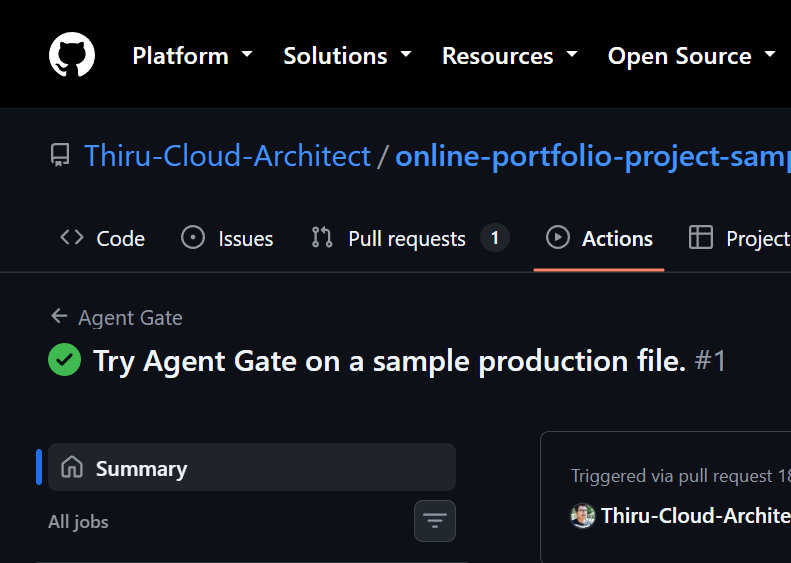
GitHub Actions run with a green check. The job on that run was named gate.
The check. The job is named gate. This run passed because it was set to comment only. A critical finding now fails the job.

Try an example

These are sample pull requests. Nothing is uploaded.

Pick a pull request

Add it to a repository

Two pieces. Critical findings fail the job. In the repository settings, require the gate check before merge.

1. Add this workflow

Save it as .github/workflows/agent-gate.yml.

name: KORV
on:
  pull_request:
permissions:
  contents: read
  pull-requests: write
jobs:
  gate:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - uses: Thiru-Cloud-Architect/agent-pr-gate-app@v1

2. Say which paths are production

Copy the sample rules to .agent-gate/policy.yaml. In this demo, production means infra/prod/** and charts/payments/**. cursor[bot] may edit docs, and may not edit production. dependabot[bot] may edit package files.

Show the sample rules